
Fraud Notice Automation
Manual to Intelligent. Fragmented to Unified. Opaque to Transparent.
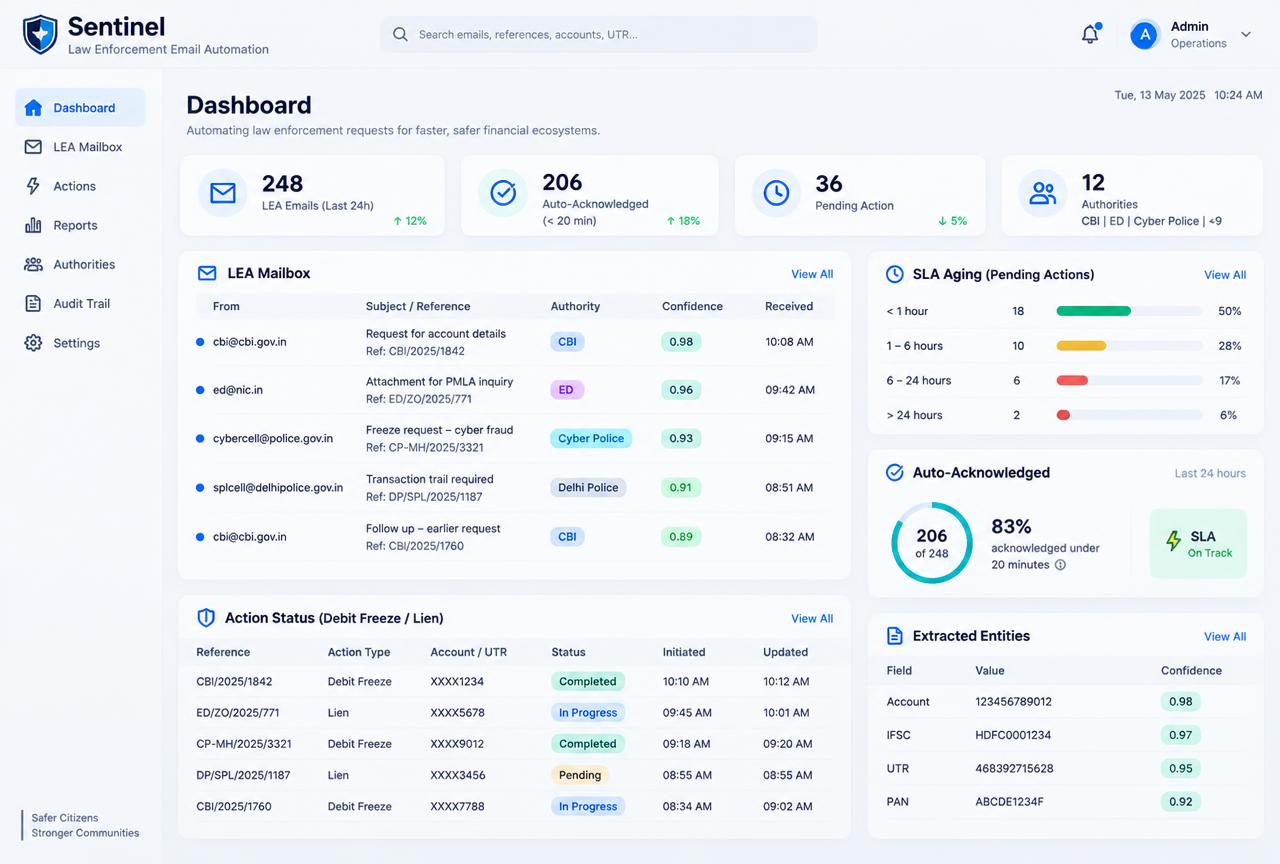
Clari5 Sentinel (Fraud Notice Automation) replaces the manual triage, routing, and response work banks do on law-enforcement requests with an on-premise, LLM-first platform that is built around Indian regulatory timelines and produces a court-admissible audit trail.
Of triage is manual today
Before automation
Average turnaround
Vs a 3–7 day RBI mandate
Man-hours a month
PSU bank estimate
To go-live
10 modules, milestone-driven
The problem Sentinel addresses
50,000 to 100,000+ LEA emails every month. Almost all handled by hand.
Emails land in multiple mailboxes with no auto-categorization, data is fetched by hand across CBS, DMS, UPI and NEFT, and there is no immutable audit trail or real-time view of volumes, aging and SLA breaches for compliance heads or CXOs.
Regulatory context
Three frameworks. One demand: faster, auditable response.
Sentinel is aligned with the RBI FREE-AI Framework, BNS 2023, RBI Circulars 2024, and PMLA / AML / CEIB.
- 4 hours — Debit freeze confirmation
- 24 hours — Account freeze or lien
- 3 days — Beneficiary details
- 5 days — Account statements
The solution
End-to-end lifecycle automation, in six stages.
Email received, deduplicated and auto-acknowledged
The 3 Pillars of end-to-end lifecycle automation
AI-first intelligence
LLM-first extraction with pattern-match and ML fallbacks, auto-learning from operator corrections, OCR for scanned images.
Compliance by design
100% auto-acknowledgement within 20 minutes, built-in court-admissible formats, immutable audit trail, color-coded SLA breach alerts (green, amber, red), and pre-loaded SOP response templates.
Enterprise architecture
On-premise with full data sovereignty in the bank's own data center, Java microservices that handle 10x volume growth, and RBAC with geographic zone assignment.
End-to-end process flow
Twelve steps. From LEA email to audit log.
Emails that are in regional languages or unreadable are routed to a manual review queue.
Phase 1
Receive and check
- 01LEA sends email
- 02Lands in bank mailbox
- 03Ingest and acknowledge
- 04Dedup check
Phase 2
Understand and act
- 05LLM/NLP extraction
- 06User validation
- 07Retrieve CBS data
- 08Execute actions
Phase 3
Respond and record
- 09Generate response
- 10Review response
- 11Send to LEA
- 12Write immutable audit log
The ten modules
Ten integrated modules. One pipeline.
Email Ingestion and Preprocessing
Captures emails from all mailboxes 24x7. Handles dedup, ticket creation, OCR, and hashing.
- Mailbox integration: IMAP, POP3, Exchange, Microsoft Graph API, Gmail, Outlook, custom SMTP connectors. Push (webhook) or scheduled pull. File-based .eml ingestion for bulk imports.
- Parsing and OCR: full header, body, and thread-ID extraction. OCR for scanned PDFs, images, and handwritten documents (95%+ accuracy). Attachments up to 50 MB with virus scanning before storage.
- Tickets and dedup: unique ticket ID (SENTINEL-YYYY-MM-DD-XXXXX). 85%+ similarity triggers auto-dedup, 60 to 85% triggers a manual review flag. Configurable 7 to 90 day window. Parent and child ticket linking.
- Compliance logging: MD5 or SHA-256 hash of every email, hash-chain audit log with tamper alerts, auto-acknowledgement within 20 minutes, retention configurable from 1 to 10 years.
ML Classification (MEC)
Classifies authority type, request type, and priority, each with a confidence score.
- Authority classification (98%+ accuracy): domain-based, covering State Cyber Police, CBI, ED, SFIO, DRI, SEBI, GST, IT, Courts, and RBI, with NLP fallback. Authority metadata drives the SLA clock and routing.
- Request type classification (F1 of 0.92 or higher): freeze, lien, statement, KYC, transaction, AOF, IP logs, CCTV. Detects multi-request emails, with a 0 to 100% confidence score.
- Priority classification (99%+ on CRITICAL): CRITICAL, HIGH, NORMAL and LOW, based on escalations, court orders and urgency keywords.
- Preprocessing: removes greetings, disclaimers, and quoted threads. Normalizes dates to ISO 8601. Detects language for regional routing.
Entity Extraction and Intent Recognition (MRI)
Extracts entities and intent with an LLM-first pipeline, including conditional logic.
- LLM-first pipeline: LLM extraction, then pattern matching (UTR, IFSC, PAN, Aadhaar), then an NER ML model. Fields below 80% confidence are flagged for human review.
- Entities extracted: account numbers, IFSC, branch code, customer name, PAN, Aadhaar, mobile, address, UTR, RRN, NEFT/RTGS references, date and time ranges, amounts, and conditional logic.
- Intent and conditions: temporary vs permanent freeze, conditional instructions ("freeze only if balance exceeds Rs 50,000"), multi-part requests and exceptions.
- Performance: 99%+ accuracy on account numbers, under 5 seconds per email, 94%+ overall extraction accuracy.
Automated Data Extraction and Action (ADE)
Pulls data from bank systems and executes freeze or lien actions via secure APIs.
- Systems: CBS, DMS, UPI platform and NEFT/RTGS.
- Action triggers: debit freeze, full freeze, lien mark via CBS write-back, and conditional freeze.
- Retrieval orchestration: statements for any date range, linked accounts via PAN or mobile, IP logs and device information, AOF and KYC from DMS, branch hard-copy routing.
- Security and resilience: REST with OAuth 2.0 and SOAP/XML fallback, TLS 1.2+, auto-retry with exponential backoff, health checks every 5 minutes, secondary source fallback.
Automated Response Generation (ARG)
Fills authority-specific templates and sends court-admissible responses.
- Template engine: authority-specific templates, dynamic placeholders, PDF, Excel and CSV outputs, and an admin console with versioning and audit trail.
- Partial and phased response: sends available data immediately; phase 2 triggers automatically when remaining data arrives — removing SLA breaches caused by slow DMS or branch responses.
- Auto-acknowledgement (under 20 minutes): includes ticket ID and expected response date from SLA rules. CEIB SOP compliant and logged immutably.
- Response audit trail: template version, data sources, recipient and timestamp, digital signature support and delivery confirmation tracking.
Dashboard and Reporting
Real-time SLA, TAT, and aging views, per mailbox or overall.
- Real-time metrics: emails received, auto vs manual split, regional language and priority counts, processing time, TAT compliance, breaches, and aging buckets (0–2, 3–5, over 5 days).
- Charts: weekly volume, 7-day SLA breach trend, authority-type distribution, and ML accuracy tracking.
- Active notices list: color-coded green (completed), amber (processing) and red (overdue), with click-through and exports.
- Reports: Daily Mailbox Processing, Monthly SLA and TAT Compliance, quarterly CXO Management Dashboard, and Cost Savings and ROI.
Queue Management
Priority queues, auto-assignment, and geo-routing.
- Queues: Intake, Manual Processing, Manual Review, and Priority.
- Processing targets: CRITICAL within 15 minutes, HIGH within 2 hours, NORMAL and LOW first-in-first-out. Priority bumps automatically as deadlines approach.
- Assignment and routing: round-robin, manual override, geographic zone routing, authority-type routing, and an Operator → Manager → Central Coordinator escalation path.
User Management and RBAC
Four-level roles, zone assignment, MFA, and a user action audit trail.
- Four roles: Viewer (PII masked), Operator (actions up to Rs 10 lakh), Manager (approval up to Rs 50 lakh, multi-zone), Admin.
- Zones: North, South, East, West, North-East. Zonal officers see only their zone; Central sees all.
- Security: MFA via email OTP, SMS or authenticator. Optional AD or LDAP. De-provisioned users keep their audit trail.
- User audit trail: logins with IP and device fingerprint, assignments, field-level data access, and approvals with old and new values.
Retention, Archival and Audit Compliance
Configurable archival with PMLA-mandated retention.
- Retention: email 3 years by default (1 to 10), audit trail 7 years under PMLA, sensitive data redacted after 1 year.
- Archival: nightly compress, AES-256 encrypt and hash; cold storage on bank NAS, tape or S3 Glacier; admin-approved retrieval with integrity checks.
- Reporting: "All LEAs Processed", "All Actions Taken" and "SLA Compliance", signed with the bank's digital certificate.
- Alignment: PMLA, RBI circulars, DPDP Act 2023, and ISO 27001.
Search and Discovery
Sub-2-second lookup by any banking identifier.
- Exact-match lookup in under 2 seconds by ticket ID, account number, PAN, mobile, UTR or RRN. Aadhaar by last 4 digits only.
- Filters: date range, authority, request type, status, TAT status and priority.
- Access control: non-owners see masked summaries; every search is logged immutably.
- Productivity: saved searches, 5+ concurrent AND filters, auto-complete and exports.
What makes Sentinel different
Six exclusive features.
Unified multi-mailbox dashboard
One view across LEA, AML, KYC, FIU, and Compliance mailboxes, with overall and per-mailbox metrics. Refreshes every 5 minutes, so the CXO view needs no drill-down.
Partial response capability
Sends available data immediately and triggers the next phase automatically when remaining data arrives.
Bidirectional workflow engine
Tracks LEA follow-ups, clarifications, and supplementary requests. The bank can request information back from the LEA within the same ticket thread.
Java microservices architecture
Each module is an independent service. Kafka queuing with no single point of failure. 10x volume growth without re-engineering.
AI auto-learning pipeline
Every operator correction retrains extraction for that bank's email patterns. Baseline accuracy of 80 to 85% grows to about 95% within 3 to 6 months.
On-premise with full data sovereignty
All 10 modules run inside the bank's data center, with no customer data leaving the perimeter. AES-256 at rest and TLS 1.2+ in transit.
09
Innovation points
Where Sentinel breaks from the market.
LLM-first classification and extraction
The LLM is the primary engine and rules sit only as fallback — the reverse of most market tools. Confidence starts at 80 to 85% at go-live and rises to 90%+ from operator feedback alone.
Three-tier entity extraction
Regex, domain validation rules, and NER for unstructured entities. A banking-domain spell-correction dictionary cleans OCR output first.
Semantic conditional-logic understanding
Parses conditional instructions, compound requests and exception carve-outs into a per-field, confidence-scored action list.
Dual-stage semantic deduplication
Catches the same case arriving via a different sender or office, preventing duplicate freeze or lien actions.
On-premise LLM deployment
Inference runs inside the bank. No email content or customer PII leaves, removing RBI data-residency exposure.
Unified cross-channel intelligence
Online (i4C/NCRP) and offline (email) notices in one system of record, with a customer-level exposure view.
Compliance-grade controls as a product primitive
Checklist-gated closure, SHA-256 audit trails with tamper detection, and maker-checker-reviewer RBAC by geography.
Reusable, bank-agnostic architecture
One 10-module pipeline across PSU, small finance, and private banks, which shortens go-live.
Institutional pedigree
Sentinel's IP inherits nearly two decades of engineering from Clari5's real-time EFRM platform.
Headline performance
Measured where it matters most.
Implementation
16 weeks to go-live.
-
1
Weeks 1–2
Foundation, DRG, and setup
Kickoff and stakeholder alignment, DRG sessions and sign-off, DC and DR provisioning, mailbox setup, 500+ sample LEA emails per category, roles and branch mapping.
-
2
Weeks 3–10
Build, train, and configure
All 10 modules built, LLM trained on the bank's sample emails, CBS, DMS, UPI and NEFT integration, templates, SLA, queue and priority configuration.
-
3
Weeks 10–12
SIT and deployment
Staging deployment, end-to-end integration testing, defect fixes and regression, RBAC setup, performance and volume testing.
-
4
Weeks 13–15
UAT and sign-off
UAT by the regulatory notices team, P1 and P2 defect resolution, formal sign-off, security review and pen test, go-live readiness.
-
5
Week 16+
Go-live and hypercare
Production go-live, 5-day parallel run, end-user training, 2-week hypercare, operations handover.
FAQs
Frequently asked questions.
Sentinel is designed to use AI to read, classify and extract information from fraud and LEA notices. It can identify relevant entities such as accounts, transaction references and other banking information. The important point is that automation does not have to mean blind automation. Confidence checks, validation rules and human review can be built into the workflow for ambiguous or sensitive cases. This helps banks improve processing speed while retaining appropriate control over high-impact decisions.
Not every notice will contain complete or consistent information. A practical fraud notice automation solution must be able to recognise exceptions rather than force every case through an automated path. Sentinel can route cases requiring additional validation or human intervention instead of treating uncertain information as fact. For a bank, this is critical. The objective is not maximum automation. It is controlled automation with minimum operational and customer risk.
Yes. The bank should remain in control of its operating and approval policies. Sentinel is designed to support workflow-based actions such as account freeze, debit freeze, lien marking or release, while allowing appropriate validation and approval controls to be applied. This supports a maker-checker-reviewer approach where required. The technology automates the process. The bank retains decision authority and accountability.
Account freezes and lien markings can have a direct impact on customers and the bank's operations. They therefore require more than simple workflow automation. Sentinel can use the information extracted from the notice and connected banking data to support the relevant action, while configurable validation and approval steps can be applied before sensitive actions are completed. It also supports the subsequent workflow when an action needs to be reviewed, released or reversed. This is particularly important as India's current cyber-fraud operating framework includes processes for grievance redressal, removal of lien markings and restoration of defrauded funds.
Sentinel is designed to work with the bank's existing technology environment rather than require a replacement of core systems. It can connect with relevant banking and enterprise systems to retrieve customer, account and transaction information and support downstream actions. This is important for large banks. Fraud notice automation should fit into the existing financial crime operating model, not create another isolated system.
Fraud and LEA notices can arrive through different channels and in different formats. Manual processing becomes difficult when teams have to interpret each notice individually. Sentinel is designed to ingest notices, classify the request and extract relevant information before initiating the appropriate workflow. This creates a more consistent process across notice types and reduces dependence on manual reading, routing and data entry.
For a financial crime process, completing the action is only part of the requirement. The bank also needs to know what was received, what was interpreted, what action was taken, who approved it and when it happened. Sentinel maintains the workflow history and audit trail across the notice lifecycle. This gives Fraud, Compliance, Risk, Internal Audit and Operations teams greater visibility into the response process and supporting evidence.
Timely reporting and response are important parts of fraud risk management. RBI's Fraud Risk Management Directions specifically establish a framework for prevention, early detection and timely reporting of fraud incidents to LEAs and regulators. Sentinel helps operational teams manage the workflow through automated intake, classification, routing, SLA tracking, escalation and response preparation. The value is not simply faster processing. It is greater consistency and visibility across the entire response lifecycle.
A fraud notice may contain incomplete identifiers or information that does not immediately match the bank's records. Sentinel is designed to support exception handling rather than silently proceed with an uncertain match. Cases can be flagged for further investigation or manual validation. This distinction matters in banking. A controlled exception is preferable to an incorrect automated action.
Before implementing fraud notice automation, a bank should assess more than processing speed. Key questions include whether the solution can accurately interpret banking and LEA notices, integrate with existing banking and financial crime systems, let the bank control automated actions and approval thresholds, handle exceptions and ambiguous cases, support full audit and traceability back to the original notice, adapt to changing regulatory and operational requirements, scale with increasing notice volumes, and measure improvements in response time, operational effort and control. The right solution should reduce manual effort without reducing governance. For a bank, that is the real test of fraud notice automation.
Explore the Clari5 platform
Cybercrime Complaint Processing
Automated NCRP complaint handling within the Golden Hour.
Learn MoreEnterprise Fraud Risk Management
The real-time EFRM platform Sentinel's engineering inherits from.
Learn MoreEvery LEA notice. Answered on time.
See how Sentinel takes a law-enforcement email from inbox to executed freeze and court-admissible response.